Breach and attack simulation
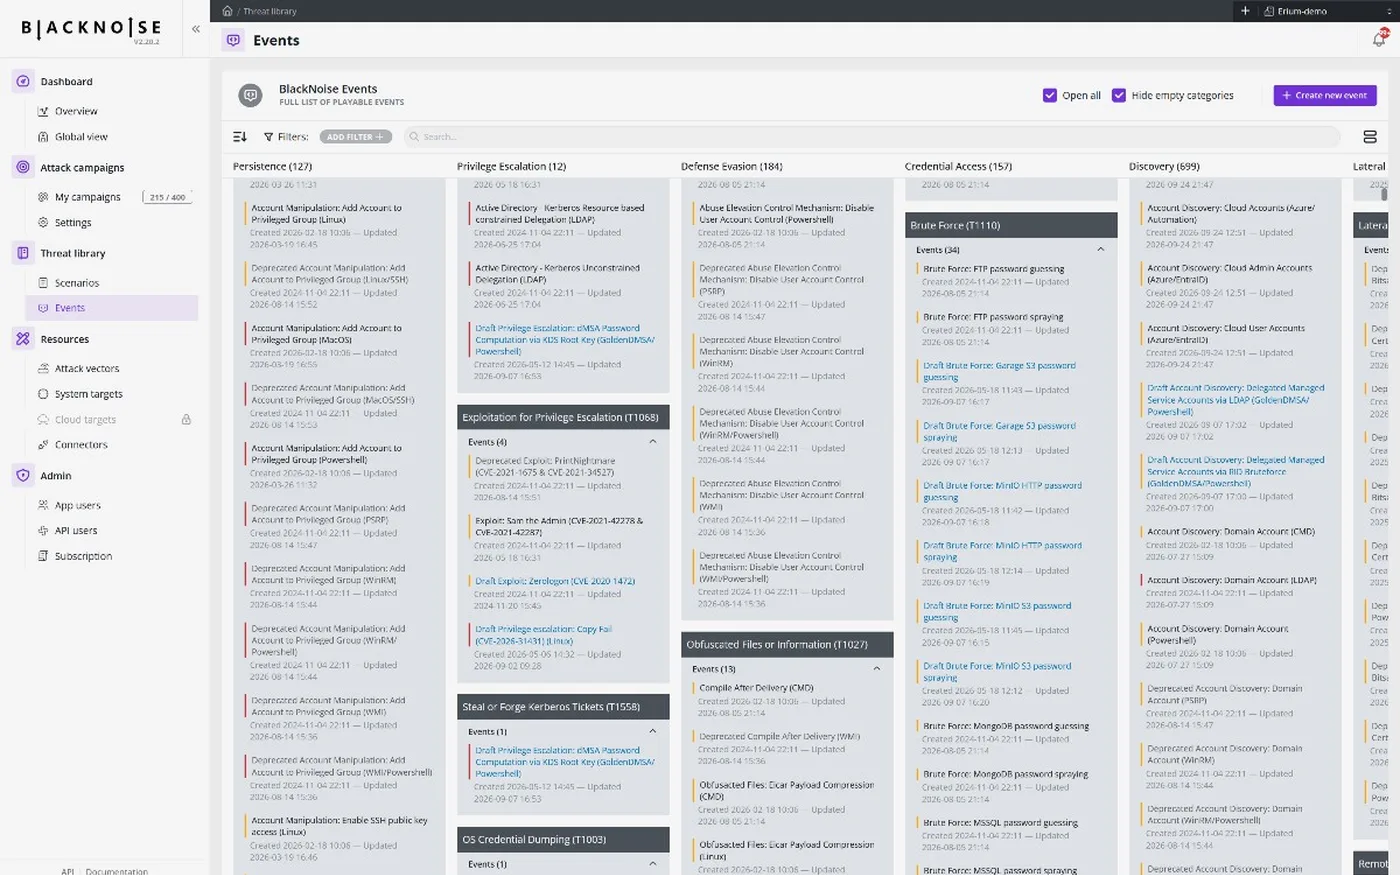
APT, ransomware, insider and AI threats, replayed against your live defenses.
BlackNoise AEV
One platform, three offensive disciplines, on your live stack.
Driven by the X-Engine: attack vectors, data, API and MCP.
APT, ransomware, insider and AI threats, replayed against your live defenses.
Threat-led testing that automates technical evidence for DORA, NIS2 and TIBER-EU.
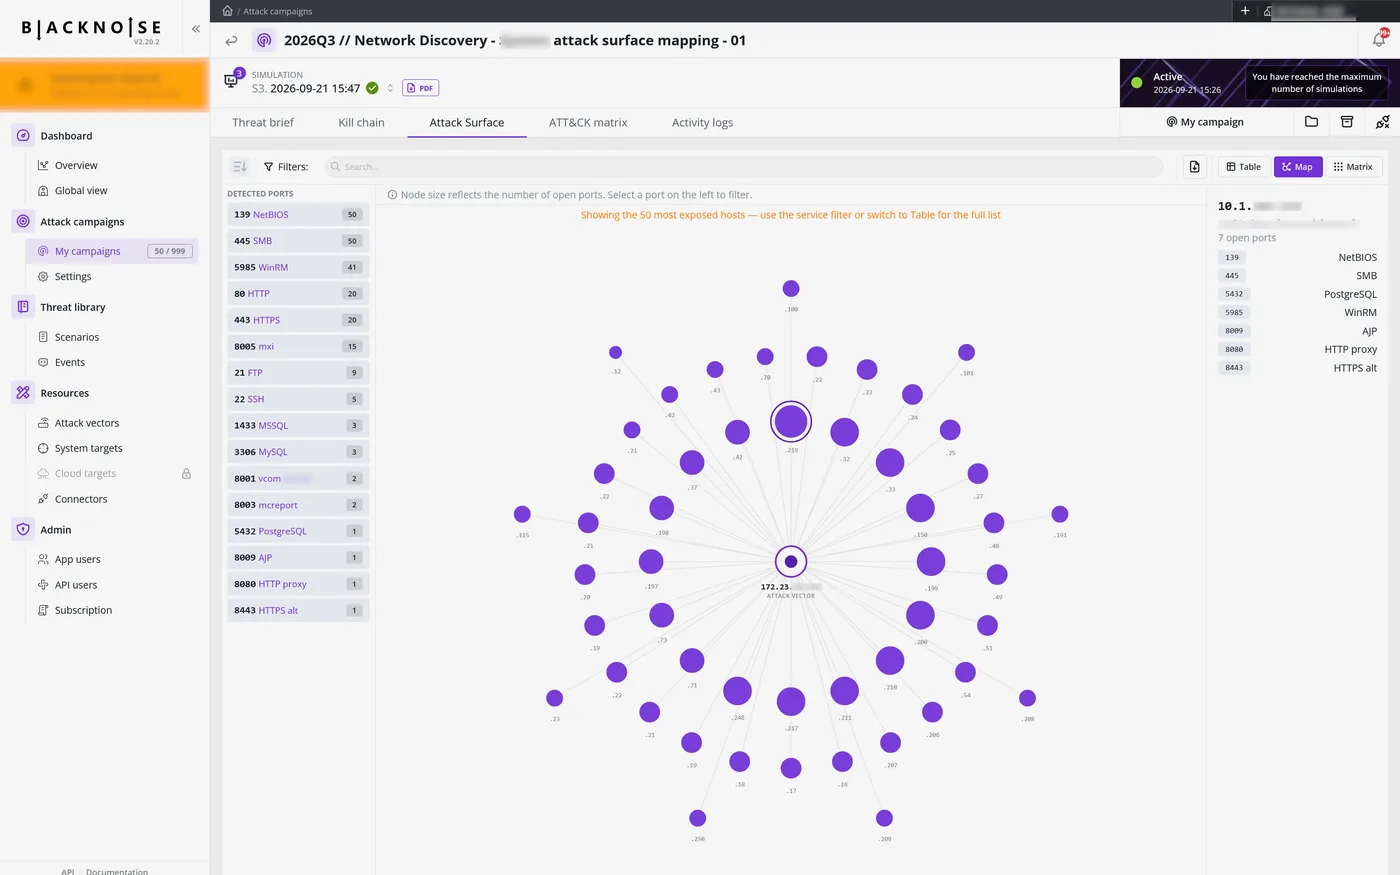
Your infrastructure seen from the attacker's side, with the Hacker View.
Continuous validation of what your defense sees, decides and does, with the evidence to prove it.
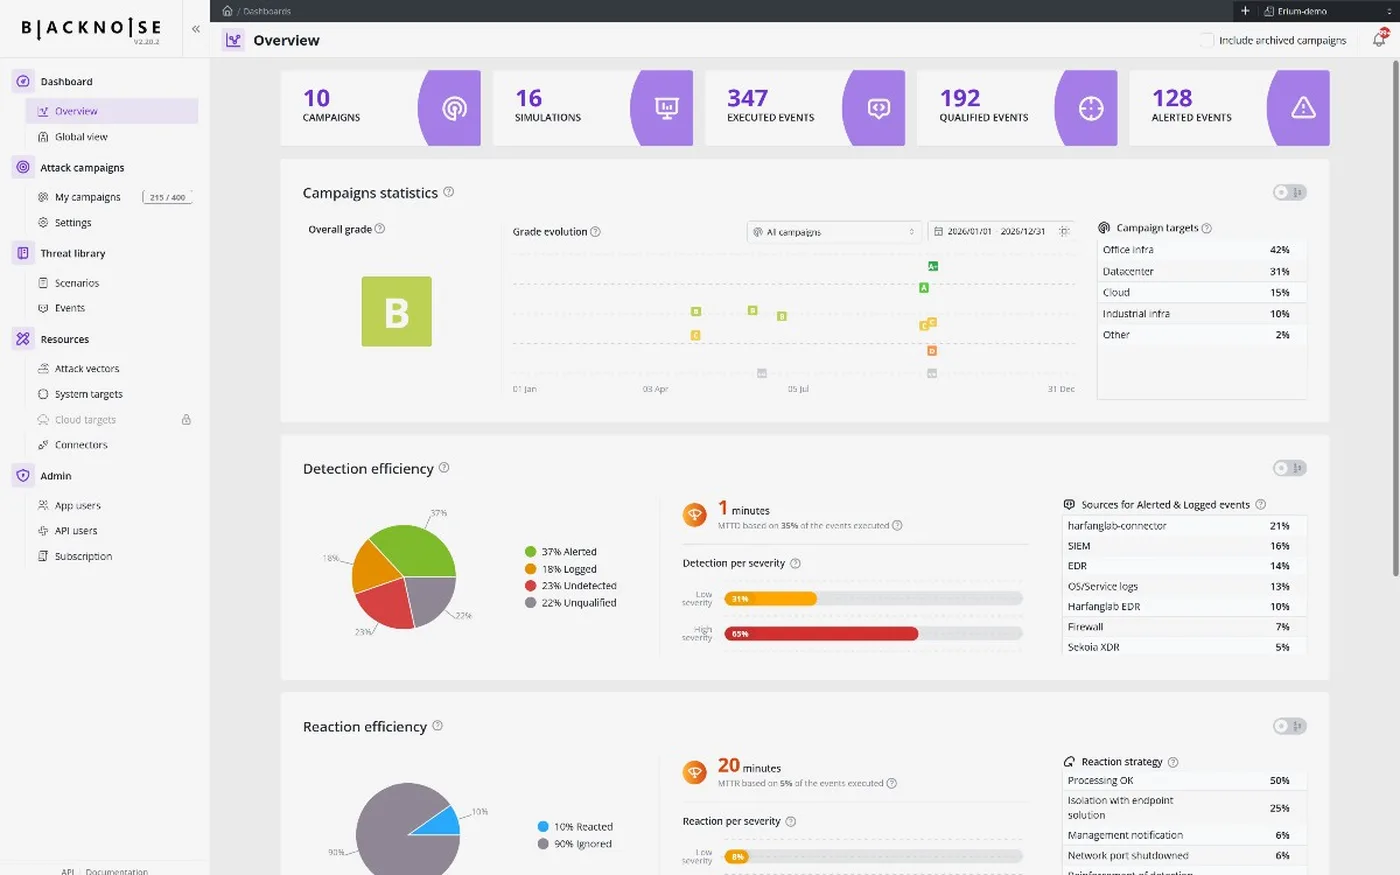
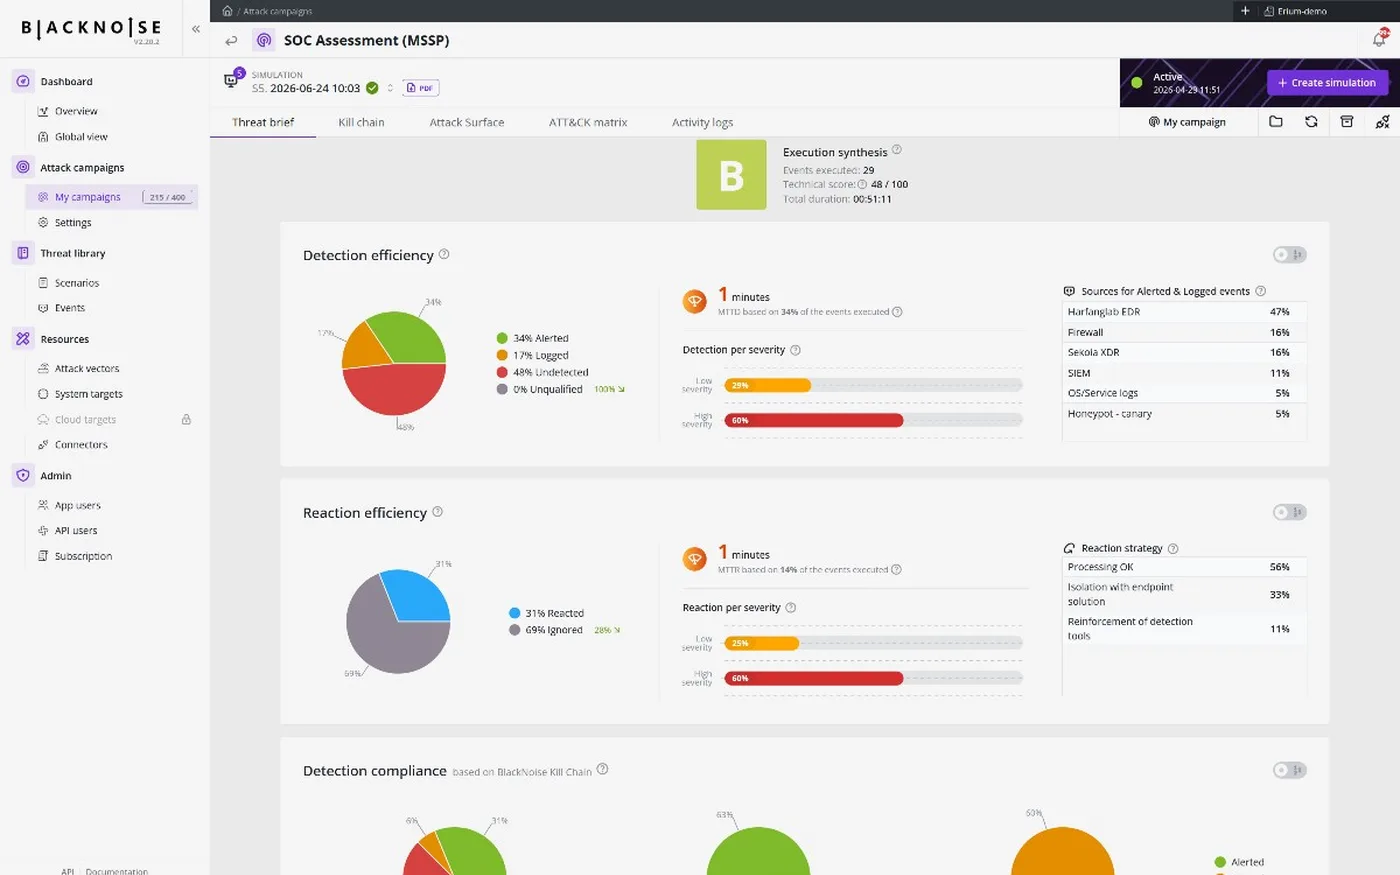
Does your stack raise the alert, and is it the right one?
OutputSignal-to-noise · coverage gaps
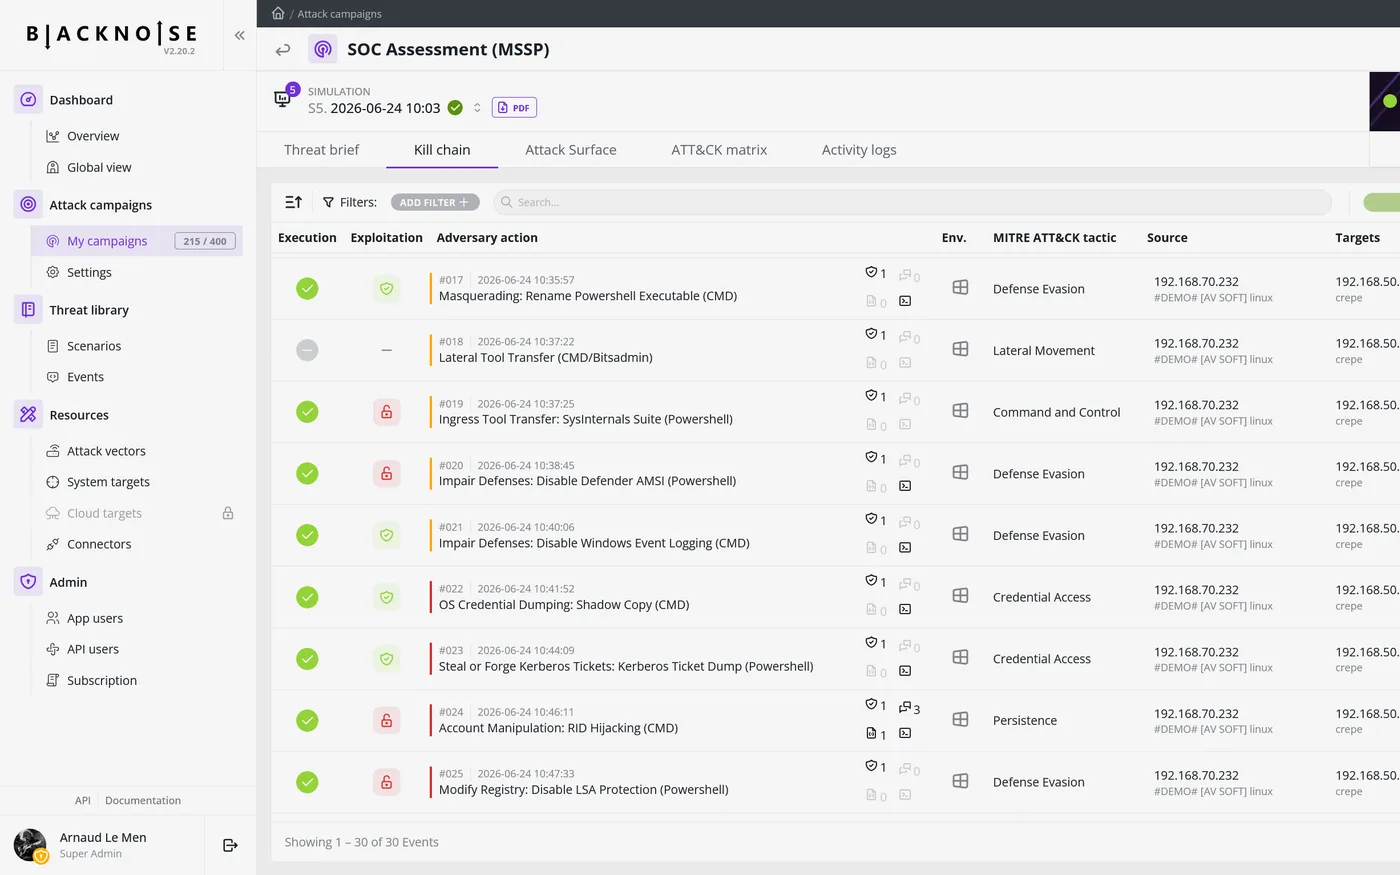
Does your SOC reach the right verdict, priority and playbook?
OutputPlaybook coverage · reaction depth
Containment time, measured end to end, run after run.
OutputMTTD · MTTA · MTTR
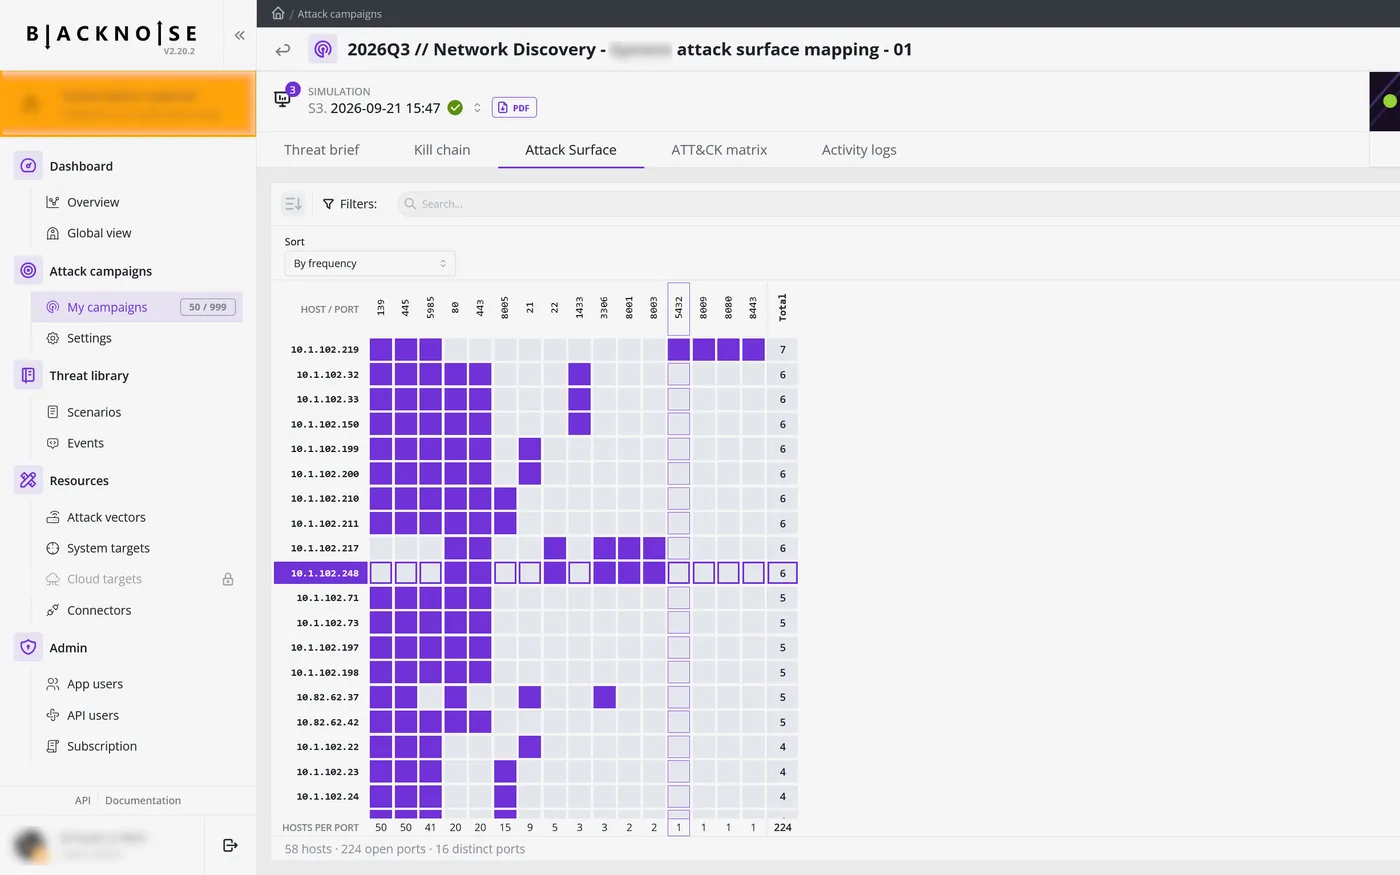
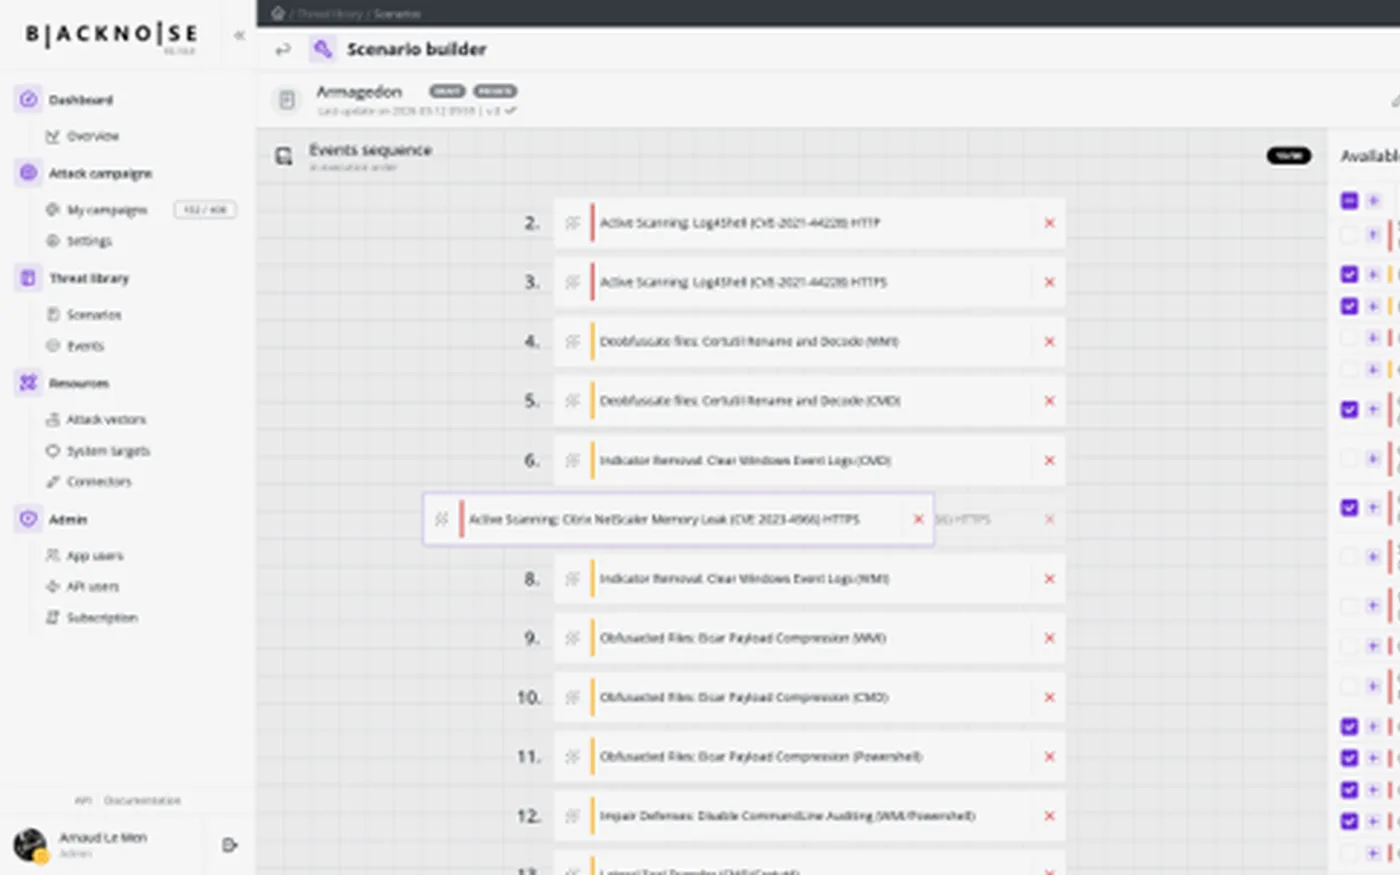
Seven views. Use the tabs or the arrows.
 HarfangLab
 Sekoia
 Gatewatcher
 Wazuh
 Microsoft Defender
 CrowdStrike
 SentinelOne
 Palo Alto
 Trend Micro
 Sophos
 Splunk
Agentless. First simulation running in minutes.
Activate virtual or physical attack vectors.
Assign attack surface and target systems.
Build, customize, schedule. Set and forget.
Track detection, MTTD and MTTR.
Add rules, improve playbooks.
 Gartner
Analyst recognition
Erium is listed as a Representative Vendor in the Gartner® Market Guide for Adversarial Exposure Validation, March 2026.
Gartner, Market Guide for Adversarial Exposure Validation, Dhivya Poole, Mitchell Schneider, Eric Ahlm, 24 March 2026. GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved. Gartner does not endorse any vendor, product or service depicted in its research publications and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner's research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.
API-first by design: every operation can be automated and plugged in.
Launch scenarios, collect results, manage targets.
Set and forget, zero manual intervention.
Push detection rules, alerts and KPIs into your tools.
Feed SIEM, XDR and SOAR with metrics and scores.
Query your BlackNoise data from your own LLM.
Prove how your response really works.
See the use case →Certificates for auditors and regulators.
See the use case →Real attack simulation inside crisis exercises.
See the use case →Drills built from what your SOC missed.
See the use case →