1. Home
  2. Use cases
  3. Cyber training & exercise

Crisis readiness, built year after year.

A multi-year program, from the SOC to the executive committee.
Cyb3r Popular Army, the fictitious attacker group In this pageThe Cyb3r Pøpular Army, our attacker

Our added value

One exercise is a snapshot. A program makes you stronger every cycle.

Phase 1

Assess

Review of your crisis organization, procedures and team maturity.

BlackNoise Skills
Phase 2 · Baseline 1

Exercise

An exercise sized to your maturity, with clear expectations: baseline 1.

BlackNoise AEV
Phase 3

Improve and maintain

Action plan, then skills maintenance on BlackNoise Skills until the next exercise.

BlackNoise Skills
Phase 4 · Baseline 2

Test harder

Baseline 1 replayed, then raised: harder and more complex.

BlackNoise AEV
Phase 5 · Baseline n

Repeat

Each cycle feeds the next. Progress visible to your board.

AEV + Skills
Maturity

What you get

Your outputs

What you measure and keep, at every baseline.

Progress you can prove

Crisis maturity

Assessed at start, compared every baseline.

Strategy and tech link

Tested on the attack actually played.

MTTD and MTTR

Time to detect, then to respond.

Action plan

Owned actions, re-tested next baseline.

Improvement over time illustrative, baselines B1 to B3

Technical team velocity

42 → 17 min

Tech and decision-maker coordination

48 → 81%

Mobilization speed

65 → 22 min

Objectives achieved

55 → 88%

What each cycle leaves you

  • Framing note and initial assessment
  • Observation notes: people, process, tech, organization
  • Attack simulation certificate, IOCs and timeline
  • Consolidated maturity report
  • Prioritized improvement plan
  • Replayable training paths and dashboard
AI assistAI-assisted reading of timelines, decisions and logs.

Our tools and our method

How we do

A real attack simulation, not a slideshow

Real attack, real telemetry: a technically measurable exercise.

Crisis training

APT, ransomware, cloud attacks and insider threats, reproduced in your real environment.

Technical assessment

DFIR, threat hunting and forensics, with detection and response measured in MTTD and MTTR.

Compliance

Evidence from threat-led penetration testing for TIBER-EU, DORA, NIS2 and PCI DSS.

100%cyber crisis simulation
80%with technical interaction
70%with executive and tech cells together
60%in an international context
90%run in one day or less

Inside the program

A credible adversary and the BlackNoise platforms make it real and measurable.

The Cyb3r Pøpular Army, a realistic threat actor

A fictitious attacker group run by Erium since 2020.
  • Credible presence on the Internet and the dark web
  • Credible TTPs, infrastructure and signatures
  • Media operations, social network activity and reputation attacks during the crisis
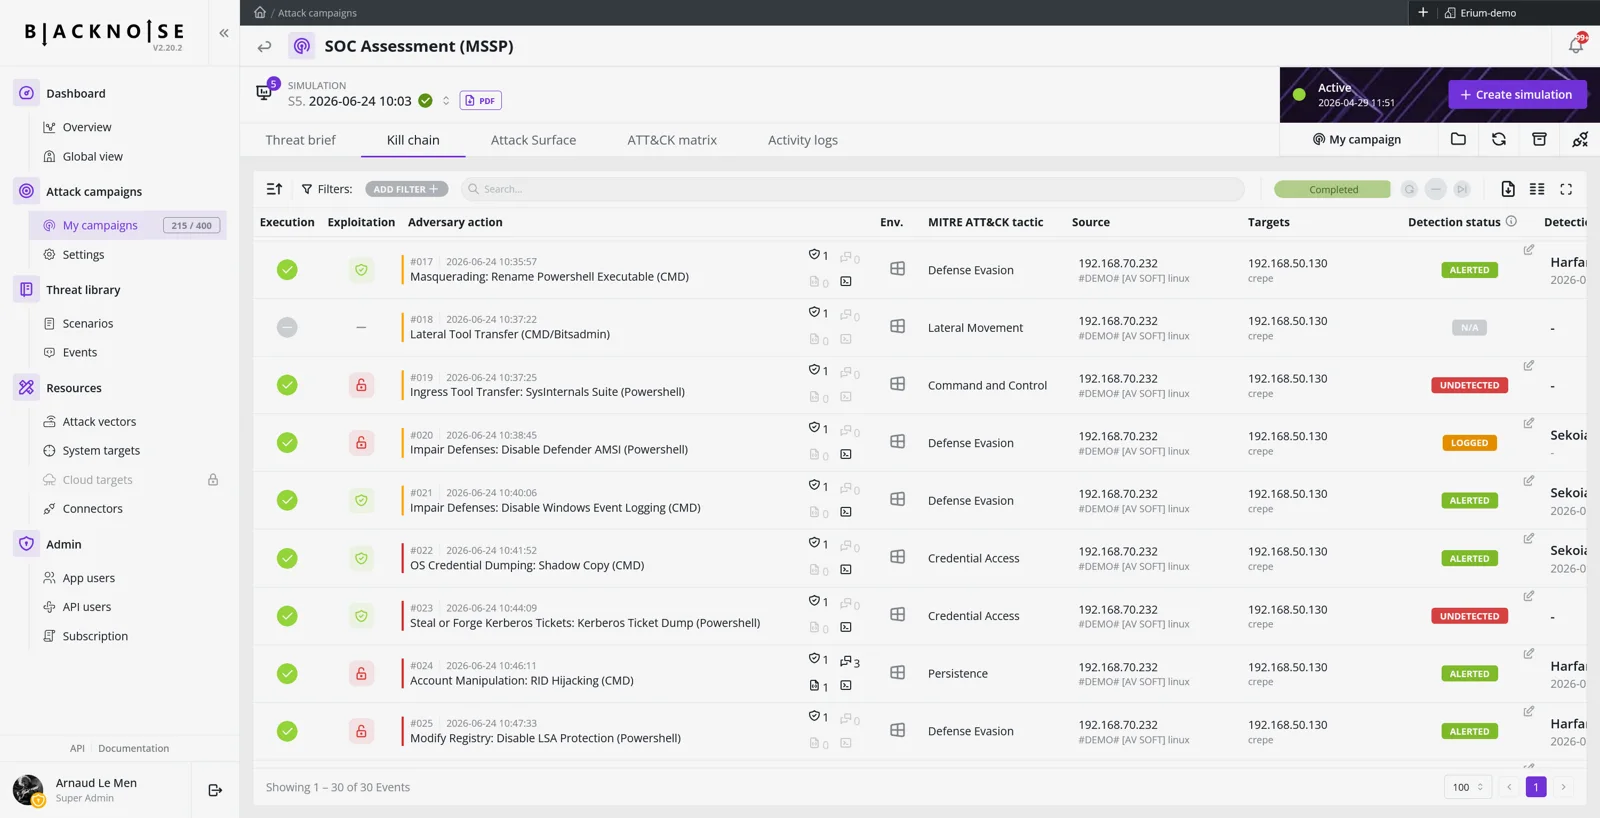
BlackNoise AEV kill chain: live execution, exploitation and detection status per adversary action

BlackNoise AEV runs the tech attack live

Real attacks, real telemetry.

  • 4,000+ adversary behaviors mapped to MITRE ATT&CK, run in your real environment
  • Detection and reaction validated on your EDR, NDR and firewalls
  • Cyberscore, MTTD and MTTR for the post-exercise analysis
BlackNoise Forge Cyber Crisis Board

BlackNoise Forge: create your crisis operations dashboard

One shared board, for exercises and the real day.
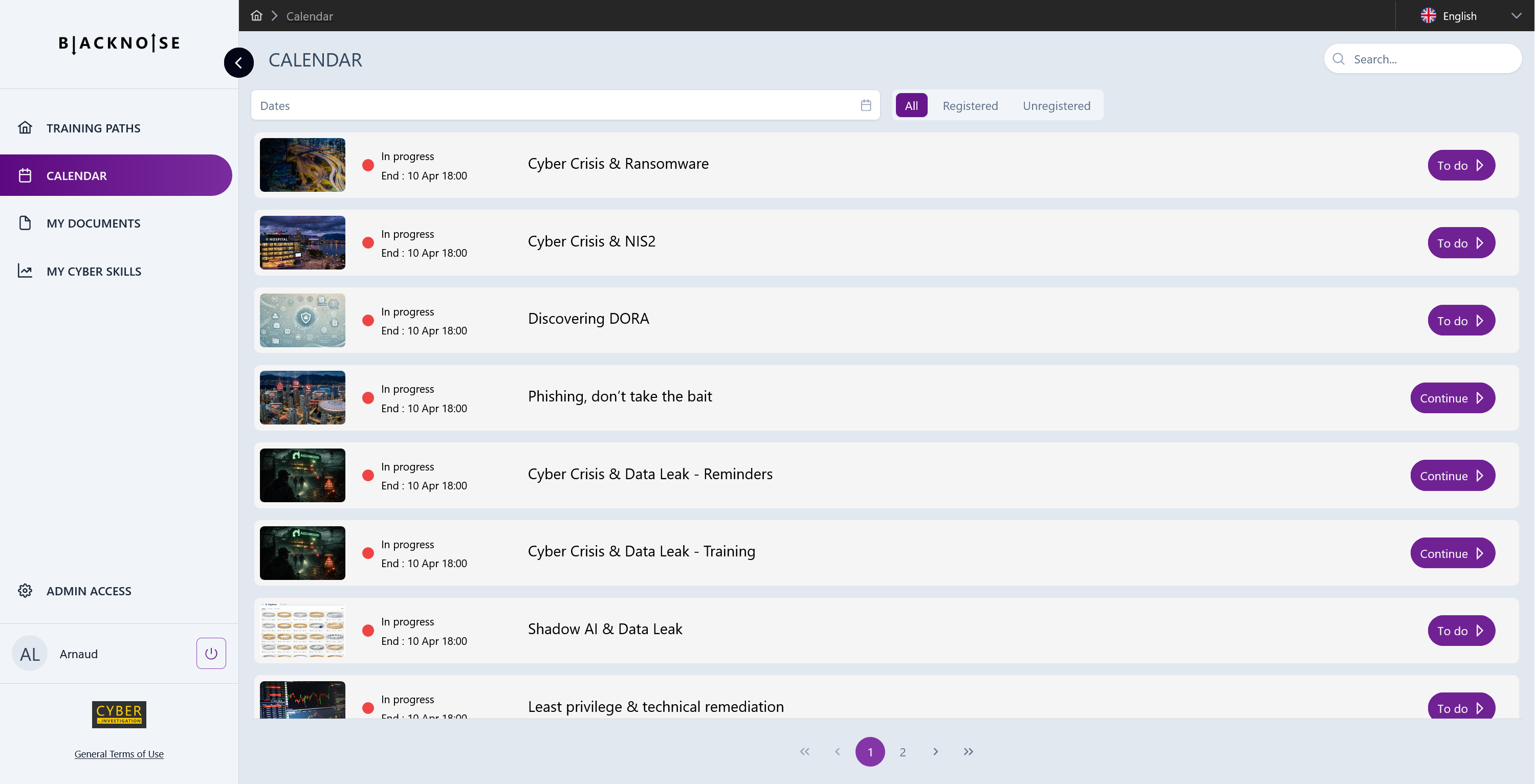
  • Crisis posture, from monitoring to major crisis
  • Share relevant data easily and immediately with every involved stakeholder
  • Log every action and decision
BlackNoise Skills crisis training calendar

BlackNoise Skills, between two major exercises

Prepare teams, then keep their reflexes alive between baselines.

  • Assessment program to map team maturity at the start
  • Before each exercise: a path in three profiles, decision, operational, business
  • After: a short, replayable scenario until the next exercise
  • Newcomers discover the processes hands-on

A library of proven crisis scenarios

Ten scenarios, tested with every cell, adapted to your sector, with no impact on production.

Massive AI-driven attackAutonomous, AI-orchestrated campaign hitting many systems at once.CPA · BlackNoise AEV
Compromise and blackmailRansomware encryption and extortion on stolen data.CPA · BlackNoise AEV
Intrusion and sabotageA wiper attack destroys systems and data.CPA · BlackNoise AEV
Massive IT outageCore services down across the organization.CPA · BlackNoise AEV
EspionageA stealthy APT, long dwell time, targeted exfiltration.CPA · BlackNoise AEV
Reputation attackDeepfakes and disinformation aimed at the brand and its leaders.CPA
Insider threatA malicious or careless insider abuses privileged access.CPA · BlackNoise AEV
Large-scale identity theftCustomer or employee identities usurped at scale.CPA
Sensitive data leakSensitive data published, blackmail and notification duties.CPA · BlackNoise AEV
VulnapocalypseA critical vulnerability exploited everywhere at once.CPA · BlackNoise AEV

In every exercise, the whole response chain

Each exercise engages every level, and tests how decisions travel between them.

Strategy

Strategic decision cell

Executive committee arbitrations: continuity, ransom, communication, regulators.

Coordination

Operational crisis cell

Situation picture, escalation, coordination of business, legal, HR and communications.

Response

IT and SecOps teams

SOC, CSIRT and IT: detection, investigation, containment and recovery.

Field

Business and sites

Degraded operations, workarounds and customer impact, where the crisis is felt.

StrategyTactical reality on the ground

Multi-site organizations: design once, replay many

One foundation, played by every region and team, measured with the same KPIs.

  1. Once

    Foundation

    Framework, scenario, storyline and training path, produced a single time.

  2. × each region

    Regional exercises

    Half-day animated sessions, run as a virtual crisis exercise in BlackNoise Skills, in each team's language.

  3. Once

    Central exercise

    One day, backed by a real attack simulation with BlackNoise AEV. Your SOC is mobilized once.

  4. Continuous

    Consolidation

    Global KPIs that reveal gaps between teams, and one prioritized improvement plan.

~70%of injects reused from one exercise to the next
½ dayper regional session
1SOC mobilization for the whole program
1set of KPIs for every team
AI assist with Dragonfl'AI module Dragonfl'AI adapts the content to each region, team and language, so costs stay under control.

Test your crisis organization before the incident.

Contact an expert