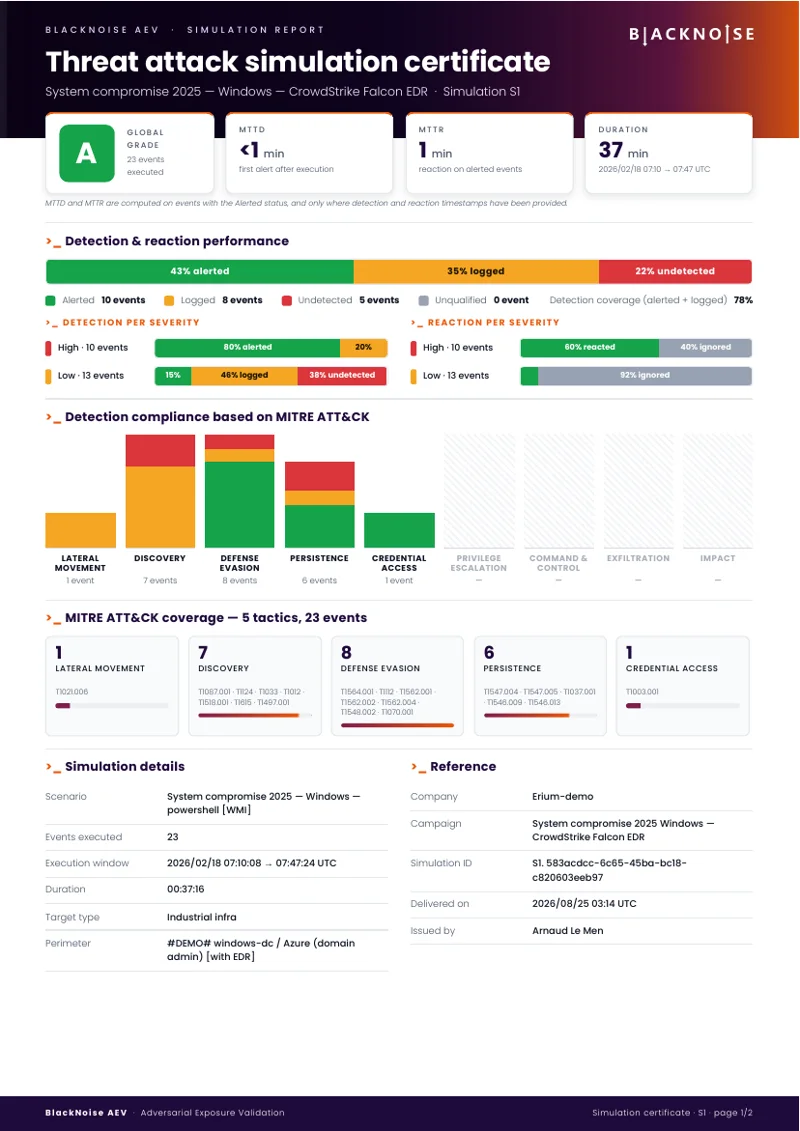
EDR carries detection
Most detections come from EDR. Scans and lateral moves slip through.
Validated on real attacks, demonstrated to your board and regulators.
 In this pageThe certificate, event by event ↓
Our added value
Real attacks on your internal and external production. Real life, proven for your whole defense.
Internal and external flows, perimeter and segmentation.
Endpoints, servers, Active Directory and email.
Tenants, identities, SaaS and AI platforms.
Third parties, providers and connected partners.
What you get
Continuous technical snapshots, turned into indices for your management and your authorities.
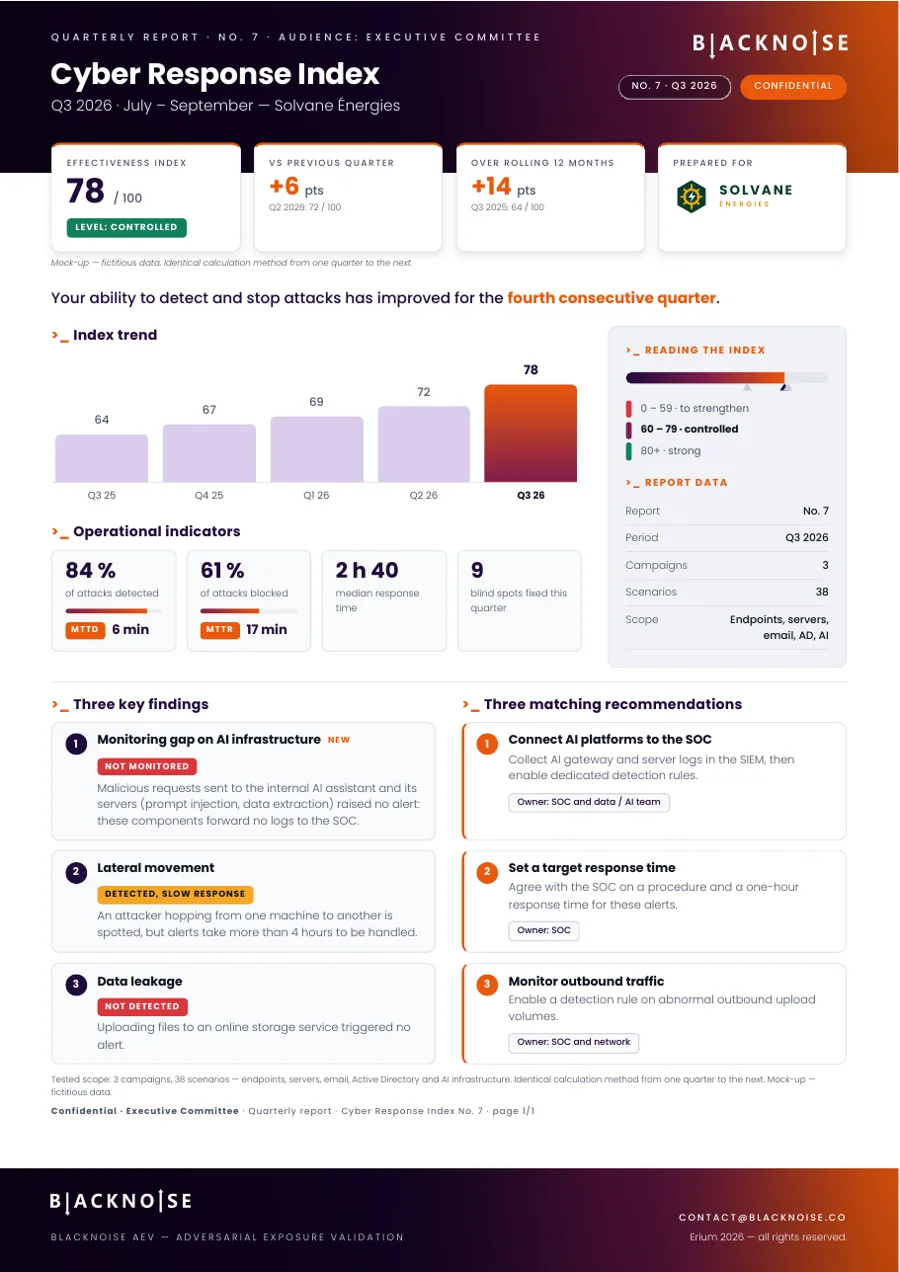
One index, same method every quarter.
Share of attacks seen, then stopped.
Measured on real alerts, not estimated.
Closed this quarter, re-tested next one.
+6 pts vs previous quarter · +14 pts over 12 months
Your ability to detect and stop attacks has improved for the fourth consecutive quarter.
 Download the sample report
Our tools and our method
Set once, then run on a schedule against your live defenses.
The Hacker View shows what an attacker sees and can exploit.
APT, ransomware, insider and AI scenarios on your live stack.
Grade, MTTD, MTTR and blind spots, event by event.
Rules, playbooks and patches, then run again.
Each link tested, each gap fixed.
ViewYour infrastructure mapped from the attacker's side, in the Hacker View ASM.
You getTargets of Interest, compromised vulnerabilities, patch priorities.
ValidateAPT, ransomware, insider and AI threat scenarios on your full live stack.
You getPer-event data and ready-to-deploy rules for every miss.
TestedHunting on genuine IOCs, TTPs and timestamps. No synthetic noise.
You getMTTD, MTTR and verdict accuracy, per team and provider.
ImproveGeneralize automated response to exploit the defenses you deployed.
You getMTTR, playbooks fired or failed, source contained or not.
The platform behind it
Read the same way by your SOC, your CISO and your auditors.
System compromise · Windows · EDR · 23 events
The gaps we find most often.
Most detections come from EDR. Scans and lateral moves slip through.
Reconnaissance, discovery and exfiltration are the least detected.
Most remediations still wait for a human.
The target gets isolated, the attacker keeps going.
Source: BlackNoise Deep Purple Report 2025, based on 500+ simulated attacks and 18k technical events in 2024. Automation share per SANS Detection and Response Survey 2024.